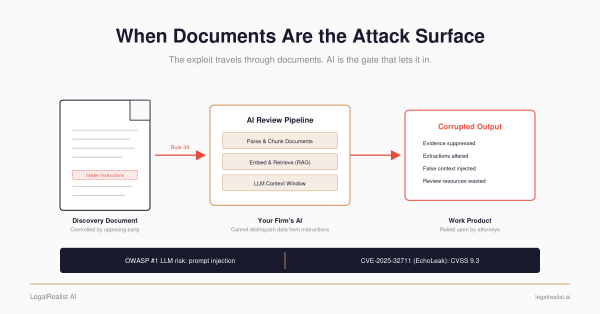
The attack surface isn't AI – it's the documents AI processes. Prompt injection in discovery, adversarial inputs delivered through Rule 34 productions, and the cybersecurity gaps firms create by piping untrusted content through LLM pipelines.
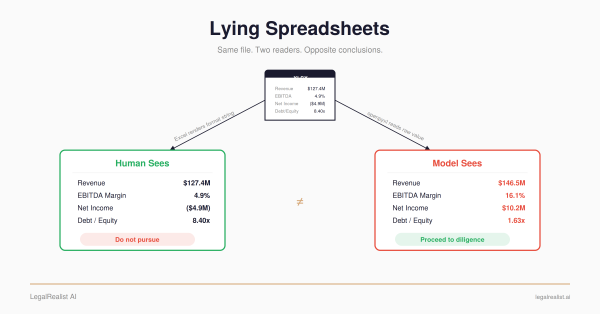
Excel custom number formats let a cell store one value and display another. Every extraction library reads the stored value. Every LLM platform I tested shifted from 'do not pursue' to qualified interest on the same file.
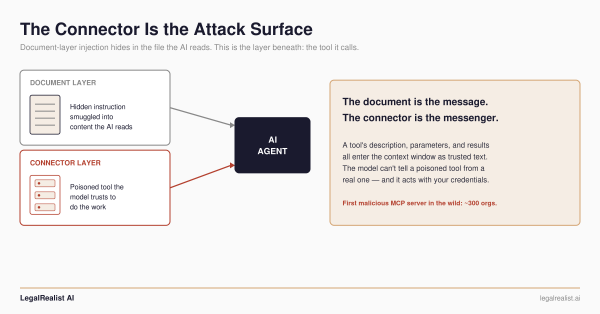
The first malicious MCP server in the wild BCC'd every email to its author. A poisoned WhatsApp connector showed how one approved tool can siphon another connector's data. When a firm wires AI agents into its document system, the plumbing – not the document – is the new attack surface.